Server & Network Hardening
Defensive systems engineering, CIS Benchmark OS lockdowns, zero-trust East-West network segmentation, and Active Directory privilege tiering to eliminate ransomware lateral movement.
GPO & DSC automated baselines
Legacy protocols eliminated
Zero cross-tier admin tokens
AES-256 GCM authenticated
Architectural Capabilities & Deliverables
Specific technical interventions, deployment baselines, and governance deliverables included in this practice.
Automated Group Policy and PowerShell DSC baselines implementing Center for Internet Security (CIS) Level 1 and Level 2 security controls across Windows Server and Linux hosts.
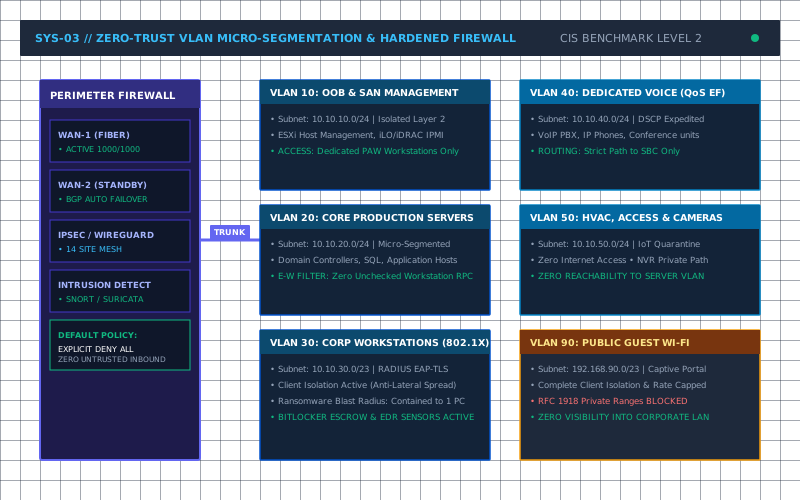
Elimination of flat corporate networks through Layer 3 inter-VLAN stateful inspection, restricting lateral traffic between endpoints, application tiers, and database engines.
Strict structural separation between Tier 0 (Domain Controllers, PKI), Tier 1 (Member Servers, Storage), and Tier 2 (Workstations), blocking Pass-the-Hash and Kerberoasting attacks.
Systematic disabling of insecure legacy protocols including SMBv1, NetBIOS over TCP/IP, LLMNR, NTLMv1, TLS 1.0/1.1, and unauthenticated RPC services.
Deployment of Windows LAPS with automated, randomized 24-character local administrator passwords escrowed cryptographically to Entra ID or Active Directory.
Centralized forwarding of Windows Security Event Logs, Sysmon telemetry, and firewall flows to an isolated, tamper-proof syslog vault for rapid incident forensics.
Supported Technology Stacks & Protocols
Vendor-neutral integration across enterprise hardware, hypervisors, and cloud environments.
- • CIS Benchmarks Level 1 & 2
- • NIST SP 800-53 Rev 5
- • MITRE ATT&CK Mitigation Matrix
- • HIPAA Security Rule § 164.312
- • Windows LAPS
- • Active Directory Administrative Tiering
- • Kerberos Armoring
- • Protected Users Group
- • Fortinet FortiOS
- • pfSense Plus Hardware Appliance
- • OPNsense Core
- • Palo Alto Networks PAN-OS
- • Sysmon (System Monitor)
- • Elastic Agent / Beats
- • Graylog Immutable Syslog
- • Snort / Suricata IDS
Commercial Contractor: Flat Subnet Remediation & Cyber Insurance Compliance
A commercial contractor was denied cyber insurance renewal due to a flat 192.168.1.0/24 subnet, shared local administrator credentials across 65 workstations, and unsegmented HVAC controller access.
Steve Cormier re-engineered the network into five isolated 802.1Q VLANs with strict firewall rules, enforced CIS Level 2 GPO baselines, deployed Microsoft LAPS, and disabled LLMNR/NBT-NS.
Achieved 100% sign-off from the cyber insurance underwriter, reduced external attack surface by 92%, and quarantined building automation systems from production corporate data.
Ready to Architect Your Server & Network Hardening?
Direct consultation with a 36-year Principal Systems Architect. Zero sales reps, zero vendor markups, and zero guesswork.